Security Essentials
Foundational assessment and hardening for smaller organizations.
- Microsoft 365 security assessment
- MFA, administrator and email protection hardening
- Device security baseline
- Prioritized remediation roadmap
Managed cybersecurity for Detroit, Michigan & Chicago
Managed cybersecurity, 24/7 threat monitoring, Microsoft 365 protection and expert IT support for growing organizations.
Around-the-clock monitoring for the systems in your agreement.
One accountable team for cybersecurity, Microsoft 365, security engineering and managed IT.
The challenge
Growing organizations face the same attacks as large enterprises — with smaller teams, tighter budgets and less time to investigate.
A convincing message, a stolen password and an attacker reading your mail.
Warnings that arrive at night and sit unread in a shared inbox.
Laptops nobody tracks and permissions nobody has reviewed.
Security features you pay for but have never turned on.
Questionnaires and renewals that ask about controls you are unsure you have.
No plan for who to call, what to shut down or how to restore.
What we do
Start with one service or combine them under a single agreement. Every engagement has a defined scope and a named point of accountability.
Around-the-clock monitoring, investigation and response coordination.
Learn moreSecure configuration, administration and support for your tenant.
Learn moreArchitecture reviews, secure configuration and hardening for Azure and hybrid.
Learn moreRemote help desk, device management and everyday IT administration.
Learn moreRisk assessments, policies, control design and audit readiness.
Learn moreCopilot readiness, AI governance and secure workflow automation.
Learn moreAlso available: 24/7 Security Operations, Virtual CISO and Incident Response.
View all servicesManaged detection & response
Our MDR service monitors the systems in your agreement around the clock, investigates what matters and coordinates the response — with actions agreed in advance.
Signals from email, identity, devices and cloud apps reviewed continuously.
Noise separated from real threats before anyone is disturbed.
Analysts establish what happened, what is affected and how.
Your named contacts receive clear findings and recommendations.
Approved actions such as isolating a device or revoking a session.
Work with your IT team, insurer and advisers through recovery.
Plain-language reports on incidents, trends and open risks.
Detections tuned and controls strengthened after every lesson.
Monitoring and response reduce risk and shorten the time to act. No provider can guarantee that every attack is prevented, and we will never claim otherwise.
Microsoft 365
You already rely on Exchange, Teams, SharePoint and OneDrive. We configure and operate the Microsoft security and management tools around them to deliver clear business outcomes.
Industries
Every sector has its own systems, risks and obligations. We bring practical, sector-specific priorities to each engagement.
Business outcomes
Good security is measured in fewer surprises, faster decisions and evidence you can show to the people who ask.
Know what is happening across email, identities and devices.
Settings applied deliberately, documented and maintained.
A plan, the right contacts and practiced decisions.
Repeatable processes for onboarding, offboarding and changes.
The right people with the right access, reviewed regularly.
Answers for customers, auditors and insurers that hold up.
Agreed scope, agreed hours and one accountable team.
How we work
A clear, manageable path from understanding your environment to running it securely — at a pace your organization can sustain.
Understand your systems, business needs and existing controls.
Identify the most important risks and the practical actions that address them.
Implement the agreed controls and services, in stages that respect how you work.
Review performance, investigate issues and refine the environment over time.
Our markets
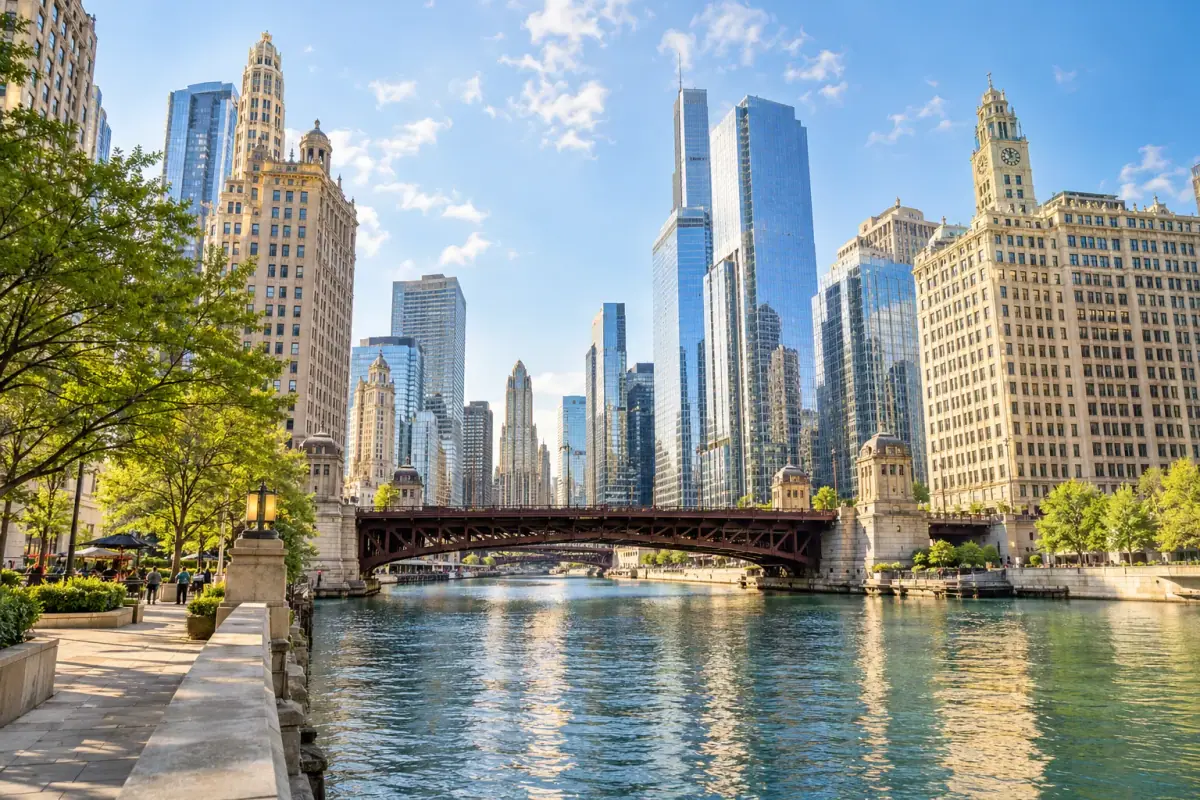
Our primary markets are Detroit, Southeast Michigan and Chicago. Services are delivered remotely, so organizations across Michigan, Illinois and the wider region receive the same standard of support.
Also see Michigan statewide services
Ways to engage
Three packaged starting points, each scoped and priced to your environment after an initial conversation.
Foundational assessment and hardening for smaller organizations.
Ongoing monitoring, security administration and response coordination.
A coordinated service combining cybersecurity and agreed managed IT functions.
Get started
Talk to Simba Cyber about your security risks, your Microsoft 365 environment and practical next steps.